TAKING UK & EU ENGAGEMENTS • UK/CET HOURS

Compliance and security,
without hiring a CISO.

For mid-market UK and European companies newly in scope for NIS2, watching the UK's Cyber Security and Resilience Bill work through Parliament, or stuck on an enterprise customer's security questionnaire: fixed-fee gap assessments, hands-on ISO 27001 delivery, and governance for the AI tools your teams already started using without waiting for a policy. Governance was never the finish line, it's the mechanism, resilience is the outcome it's supposed to produce. Built on what I actually find, not a fear campaign.

25 yrs IT & Cyber
0 → 1 AI Governance
10,000:1 CISO Ratio
100% Fixed-Fee
ISO/IEC 27001 Lead Auditor
CISSP Certified
25 Yrs in IT, Cyber & Infra
Swipe to explore
// PRACTICE AREAS

Capabilities & Advisory Pillars

02 / 06
Accreditation

ISO/IEC 27001 & GRC Architecture

I run the whole process myself, from the first gap assessment through the stage 2 audit. I rebuild your vendor and licensing footprint at the same time, not after, so the certification ends up paying for itself instead of just costing you.

Statement of Applicability & Risk Register
Tailored ISMS policy documentation & control implementation
Internal audit defence & external auditor representation
More on ISO 27001 implementation →
Compliance

NIS2, GDPR & UK Cyber Resilience Readiness

NIS2 put incident reporting clocks and personal accountability on management boards across the EU, and the UK's Cyber Security and Resilience Bill brings the same shape of rules to managed service providers and critical suppliers. If a customer contract hinges on a NIS2 or GDPR questionnaire you can't answer yet, this is the fast version: a gap evaluation that tells you exactly what's missing, before an auditor, an insurer, or that customer does.

Incident reporting playbooks: NIS2 24-hour early warning, GDPR 72-hour breach notification
Supply-chain & third-party risk validation (TPRM)
Management body accountability & sign-off (NIS2 Art. 20)
Also available: Essential Eight & Privacy Act for Australian clients
More on NIS2 & GDPR readiness →
Emerging Tech

AI Governance & Safe Enablement

Your team is already using AI. Banning it just pushes it underground. I build the acceptable-use rules, the data boundaries, and an actual sign-off process instead, so people can use the tools without you finding out what went wrong after the fact. I also map the tools you actually use against the EU AI Act, so you know what's in scope well before the high-risk rules land in December 2027.

Shadow AI discovery audit & corporate data leakage boundaries
EU AI Act risk classification & transparency obligations review
Fast-track AI deployment risk assessment & sign-off protocol
LLM data protection & intellectual property safeguards
More on EU AI Act & AI governance →
Executive

Fractional vCISO & Board Advisory

I sit in your leadership meetings, not beside them. Board updates, the security questionnaire blocking a deal, the incident plan nobody's tested yet, the vendor who keeps missing their own SLA. That's the job.

Quarterly Board & Audit Committee security risk briefings
High-stakes sales deal support & vendor security questionnaires
Incident response playbooks & tabletop exercises, tested before you need them
More on the fractional CISO service →
// PROVEN OUTCOMES

Track Record & Evidence

03 / 06
// ISO 27001 & GRC PROGRAMME REF: 27001-ENG

A certification programme that paid for itself

I led a full ISO/IEC 27001 programme end to end, from the first gap assessment through the stage 2 audit, including GDPR-aligned data protection controls. Instead of letting the compliance spend stack on top of what was already there, I rebuilt the software licensing and vendor footprint at the same time as the audit, not after it.

> Licensing and vendor footprint rebuilt in parallel with the audit, so the certification paid for itself
// AI GOVERNANCE ARCHITECTURE REF: AI-GOV-01

An enterprise AI governance framework, built from zero

I designed and built an AI governance framework from a standing start, for a business already using commercial AI tools faster than anyone had written a policy for it. Acceptable use standards, real data handling boundaries, and a sign-off process fast enough that people actually used it, so engineers kept moving and nothing walked out the door in a prompt.

> 0 → 1 framework established; resolved ungoverned shadow AI usage without slowing development pace
// FRACTIONAL LEADERSHIP ADVANTAGE REF: CISO-MARKET

There aren't enough CISOs to go around

Roughly 35,000 full-time CISOs work worldwide against an estimated 359 million businesses, a 10,000-to-1 ratio. Nearly every Fortune 500 company has one. Almost none of the mid-sized businesses that actually make up the global economy do. The 2026 SANS/GIAC Workforce Report says AI is making this worse, not better, automating away the junior analyst roles that used to train the next generation. Fractional leadership isn't the cheap substitute for a real CISO. For most of this market, it's the only version that's actually available.

> 10,000:1 global business-to-CISO ratio (Sophos / Cybersecurity Ventures 2026 CISO Market Study)
// FOUNDER & ADVISORY

About Haden McAlpine

04 / 06
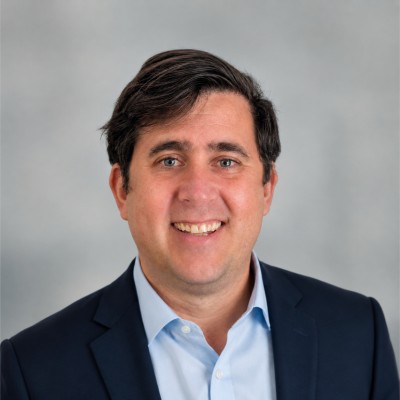
Haden McAlpine

Haden McAlpine

Principal Cyber & AI Advisor
  • Credentials CISSP • ISO/IEC 27001 Lead Auditor
  • Track GRC • Security • AI
  • Experience 25 Years IT, Cyber, Cloud & Infra
  • Background Head of Cyber Security & Infra
  • Base Sydney • UK & EU Engagements

I've sat in the room while a vendor tried to sell a board a six-figure platform to fix a problem a spreadsheet and a firm email would have solved. Twenty-five years in IT, cyber security, cloud, and infrastructure across retail, manufacturing, and financial services taught me that lesson more than once.

I've also watched consultants walk in, hand over a slide deck built to scare a board into a bigger contract, and walk out again before anyone had to actually run the thing they sold. That's not how I work. If I'm recommending something, it's usually because I've already built the version of it that gets used, not just the version that looks good in a steering committee meeting.

“Honesty and a straight answer aren't a selling point here, they're just what's left once you cut the fear-mongering out of the pitch.”

I ran a full ISO 27001 programme end to end and rebuilt the vendor and licensing footprint while doing it, not after, because the certification work and the vendor cleanup were always going to touch the same contracts anyway. I also built an AI governance framework from a standing start for a business that had already started using AI tools faster than anyone had written a policy for it. CISSP and ISO/IEC 27001 Lead Auditor, still the person who reads the vendor contract before anyone signs it.

Full profile
// ENGAGEMENT ARCHITECTURE

Structured, Predictable, High-Leverage

05 / 06
01

Fixed-Fee 3-Week Diagnostic

Three weeks, fixed fee, no surprise invoice at the end. I go through your infrastructure, access controls, vendor list, and whatever AI tools people are actually using, then hand you a straight gap list and a roadmap ranked by what actually matters first. Most of it runs remotely in UK and Central European business hours, with on-site days booked as a block when being in the room matters.

02

Targeted Remediation & Delivery

I write the policies, put in the technical controls that actually matter, handle the vendor consolidation myself, and get your team ready for whatever's next, a customer's due diligence or a formal audit.

03

Fractional vCISO Retainer

Ongoing, not occasional. Board reporting, the security questionnaires that land on your desk at the worst time, AI risk reviews as new tools show up, and an incident plan your team has already rehearsed, so nobody's improvising when something actually breaks.

// INITIATE ADVISORY

Schedule Executive Consultation

06 / 06

Confidential Advisory Intake

Submit your enquiry below. Submissions are encrypted, and I review every one myself, under strict confidentiality.

Cloudflare Protected • Strict Mutual NDA

I only use what you send here to reply to you. Privacy notice.

Direct Founder Access

You speak directly with Haden McAlpine, not an account executive or junior consultant.

24-Hour Response SLA

Enquiries reviewed and answered with strategic clarity within one business day.

Strict Mutual NDA

Confidentiality agreements supported prior to discussing proprietary architecture.